One signature, five attachments
The signature contained no files at all, yet Gmail counted five attachments. The cause was base64 image data, and the fix came down to deciding where the images actually live.
- HTML email
- Gmail
- Debugging
A message left my outbox with nothing attached to it, and Gmail still filed it under five attachments. The phone made it more obvious, which is what sent me looking. A signature should not be able to add attachments to a message.
Five images, five attachments
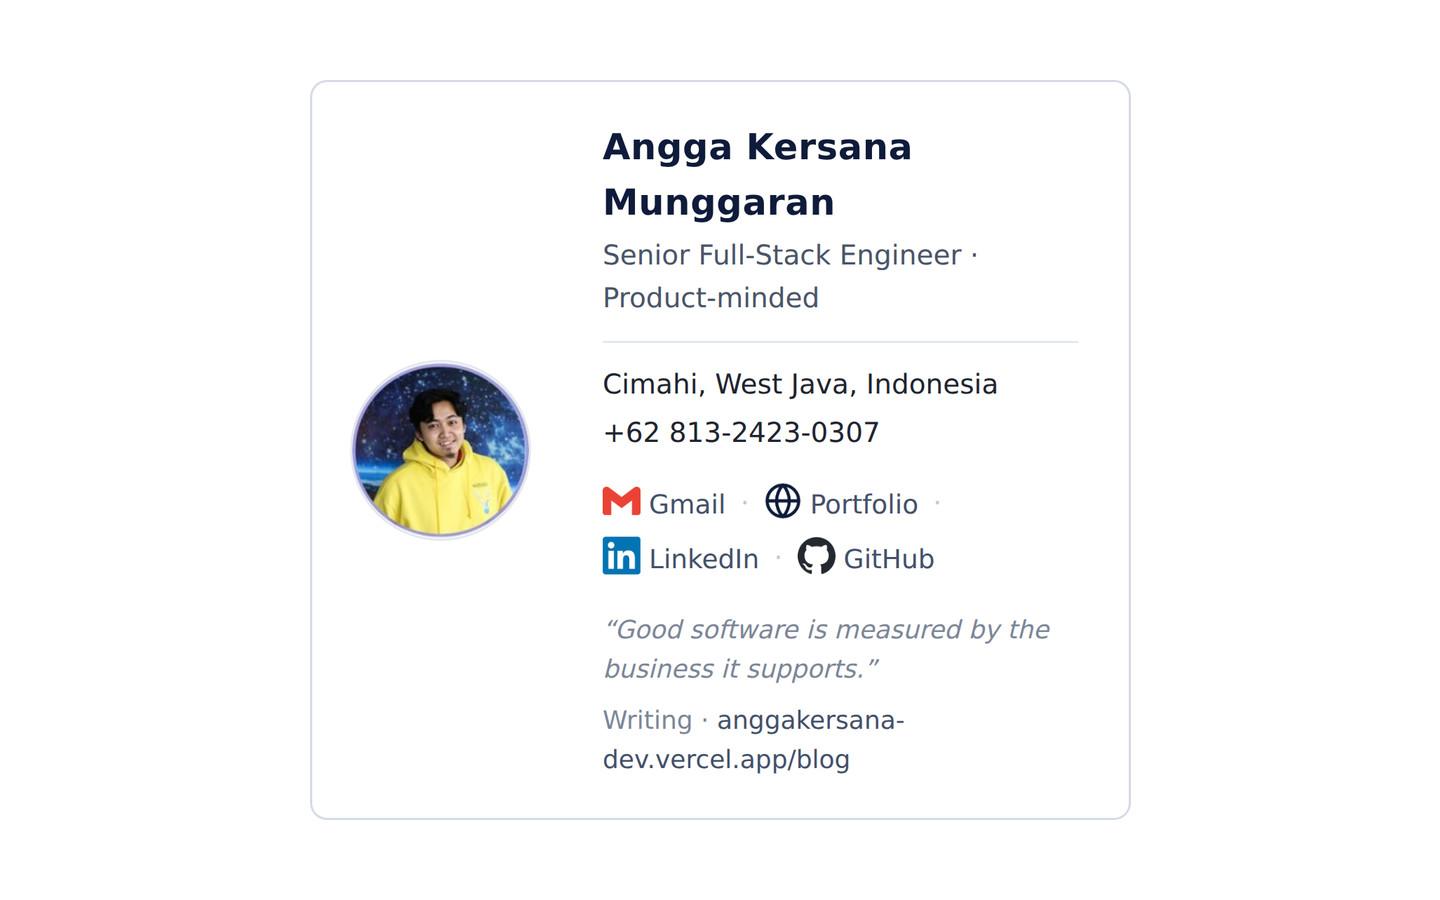
The signature is one table. Inside it there is a portrait and four small icons for the links, which comes to five images, and five is exactly the number Gmail was reporting. The count was never about files. It was about how those five images were being carried.
Why base64 looked like a good idea
Every image was pasted in as a data:image/png;base64, string. For a signature that is genuinely tempting. The whole thing lives in one blob of HTML, there is no second file to host, and nothing can 404 because nothing is being fetched from anywhere.
The costs turn up later, and there are three of them.
- Gmail does not render them. A data URI in a signature body is either stripped out or pulled into an attachment, which is what those five chips were.
- They are about a third larger. Base64 maps three bytes onto four characters, so every image carries that overhead, and the string is copied into every message you send.
- Nothing is cached. A hosted image is fetched once and reused across a thread. Embedded data is re-sent in full every single time.
The version that caused it
<img src="data:image/png;base64,iVBORw0KGgoAAAANSUhEUgAAAEAAAABACAYAAACqaXHeAAAAAXNSR0IArs4c6QA..." width="18" height="18" alt="" /><img src="https://anggakersana-dev.vercel.app/signature/gmail.png" width="18" height="18" border="0" alt=""
style="width:18px;height:18px;border:0;display:inline-block;vertical-align:-3px;margin-right:4px;" />Where the images could live instead
Once the images have to be fetched rather than embedded, the only real question left is who serves them. I went through the options.
- A path on my own machine.
src="/signature/photo.jpg"resolves against the recipient's computer, not mine, so it points at nothing. - Google Drive. The obvious candidate, since the files were already sitting there. I tested it rather than trusting what I remembered, and the numbers are below.
- A general image host. This works, but the URL is rented. A host can rate limit it, rename it, or shut down, and by then the signature is sitting in mail you can no longer edit.
- My own domain. Already paid for, already deployed, and the only option here where I control the path for as long as I keep the domain.
I tested the Drive URLs instead of repeating what I read
The advice online says Drive direct links were killed in January 2024 and now return a 403. That is not what happened when I checked. I took one public file and asked for it three ways, once with a plain curl user agent and again with the user agent Gmail's image proxy sends.
https://drive.google.com/uc?export=view&id=FILE_ID
https://drive.google.com/thumbnail?id=FILE_ID&sz=w1000
https://lh3.googleusercontent.com/d/FILE_IDuc?export=viewanswered 200 and sent back a PDF. The first bytes of the body are%PDF-1.5, and the content type shifted with the user agent,application/octet-streamfor curl andapplication/pdffor the proxy, across a byte count that never moved. Animgtag cannot render a PDF, so this is the form that used to work and now quietly does not.thumbnailworks. It answered 200 with a real PNG of 785 KB, after redirecting tolh3.lh3works and skips the redirect. It served a real PNG of 862 KB, and it accepts the sizing suffixes Google Photos uses, so=w200brought the same image down to 45 KB.
So Drive is not dead. Drive works, through an endpoint that appears in no documentation, and that is the whole problem. The /uc form was undocumented too, and people leaned on it for years before it started returning PDFs with no announcement. Choosing lh3 today means betting that Google keeps an undocumented path alive for as long as your old emails stay in other people's inboxes. There is a second exposure sitting underneath it: the image is a file in a Drive folder, so moving that file to the trash or having it flagged breaks the signature retroactively in every message you have already sent.
What I ended up with
The images are files in the site's public directory, served over HTTPS from the same domain as everything else. Nothing new to pay for, nothing new to keep alive, and a path I chose.
The trade is that the path is now a promise. Those five URLs are sitting in mail that has already been delivered and cannot be edited, so renaming or moving one of those files breaks the image in every message that used it. That is worth writing down next to the files, which is what I did.
What the clients do to the markup anyway
- Gmail does not fetch your image in front of the reader. It rewrites the URL and serves it through its own proxy, so your logs show Google rather than the person who opened the message.
- Outlook ignores a fair amount of CSS, so
border="0"andbgcolorstill earn their place as attributes rather than style declarations. - Some clients drop
border-radius, so the circular crop of the portrait is baked into the pixels instead of being asked for in CSS. - There is no stylesheet. Everything is a table with inline styles, because that is the only vocabulary every client agrees on.
The counting pixel, and how much it can tell you
Once the images live on a domain you control, the next idea arrives on its own. Put a tiny image in the signature pointing at an endpoint you own, count the requests, and every fetch is someone opening your email. This one works, and I have shipped it. In a sending system I worked on, every outgoing email carried a pixel aimed at an endpoint that recorded the first open and ignored every one after it.
<img src="https://example.com/api/open/RECIPIENT_CODE/pixel.gif"
width="1" height="1" alt="" border="0" />export async function GET(request, { params }) {
const { code } = await params;
// No-op when this recipient already has a timestamp.
await recordFirstOpen(code);
return new Response(PIXEL, {
headers: {
"Content-Type": "image/gif",
"Cache-Control": "no-store, no-cache, must-revalidate",
},
});
}Two details are doing the work there. The code in the URL identifies the recipient, so the count tells you who opened rather than only how many. And the write is guarded, so a second fetch for the same recipient does not inflate the number.
A signature can have the second of those and not the first. It is one blob of HTML pasted into one settings box, so the pixel URL is identical in every message you send. There is no per-recipient code to put in the path, which means no attribution. What you get is a running total across every email you have ever sent, and no way to tell which message moved it.
The other half of the problem is what a fetch actually means.
- Gmail does not let the reader's device fetch your image. It fetches the URL itself through a proxy on
googleusercontent.com, caches it, and serves the reader the cached copy. The request that reaches you is Google's, carrying theGoogleImageProxyuser agent, which is the same agent I used to test the Drive URLs earlier in this post. It can arrive at delivery time rather than reading time. - Apple goes further. Mail Privacy Protection, on by default since iOS 15 in 2021, pulls every remote image through Apple's servers whether or not the message is ever opened, and it applies to any account read in the Apple Mail app rather than only to Apple addresses. By 2025 Apple was being reported at more than half of all opens recorded across the industry, which is a long way of saying that a large share of the opens everyone counts never involved a person.
- Caching pulls the number down in the other direction. A repeat view is often served from a cache, so it never reaches the endpoint at all. That is part of why the first-open guard above is cheap: most of the duplicates were never going to arrive anyway.
- And images are blocked by default in plenty of clients until the reader asks for them, so a genuine read can produce nothing.
So the honest conclusion is not that the endpoint fails. It counts fetches, and a fetch is not always a read. In a sending system, where the per-recipient code lets you attribute each one and the first-open guard keeps it from drifting, that is still a useful directional signal, which is why it earns its place in production. In a signature, where you also lose the attribution, what is left is a number that goes up. It is also worth a look before you ship one, since European privacy rules treat a tracking pixel as a different thing from the email carrying it.
The half of the problem that is not in the HTML
Fixing the HTML did not fix the phone, and this is the part I would have missed if I had stopped at the markup. The Gmail app keeps its own signature setting, separate from the one in Gmail on the web, and it accepts plain text only. The two do not sync. You can have a carefully built HTML signature in the browser and a completely different, much older one on the phone, and nothing anywhere tells you that.
So a signature is not one artifact. It is two, configured in two places, and the phone one cannot hold a single image. Set both deliberately.
What I would tell someone starting this
- Never embed the images. A
data:URI does not survive Gmail, and it makes every message you send larger. - Host the images somewhere you control, and treat the URL as permanent.
- Design for the narrowest column first. If the links reflow onto two rows and nothing overflows, the wide version takes care of itself.
- Set the mobile signature too. It is plain text, and it is the one people forget.
- Check the result in a client you do not control, because your own browser is the most forgiving place you will test it.
A signature is a small piece of HTML that nobody looks at twice, which is exactly why it is worth getting right once. Mine now travels in every message I send, and it stopped announcing itself as five attachments the moment the images had somewhere real to live.